
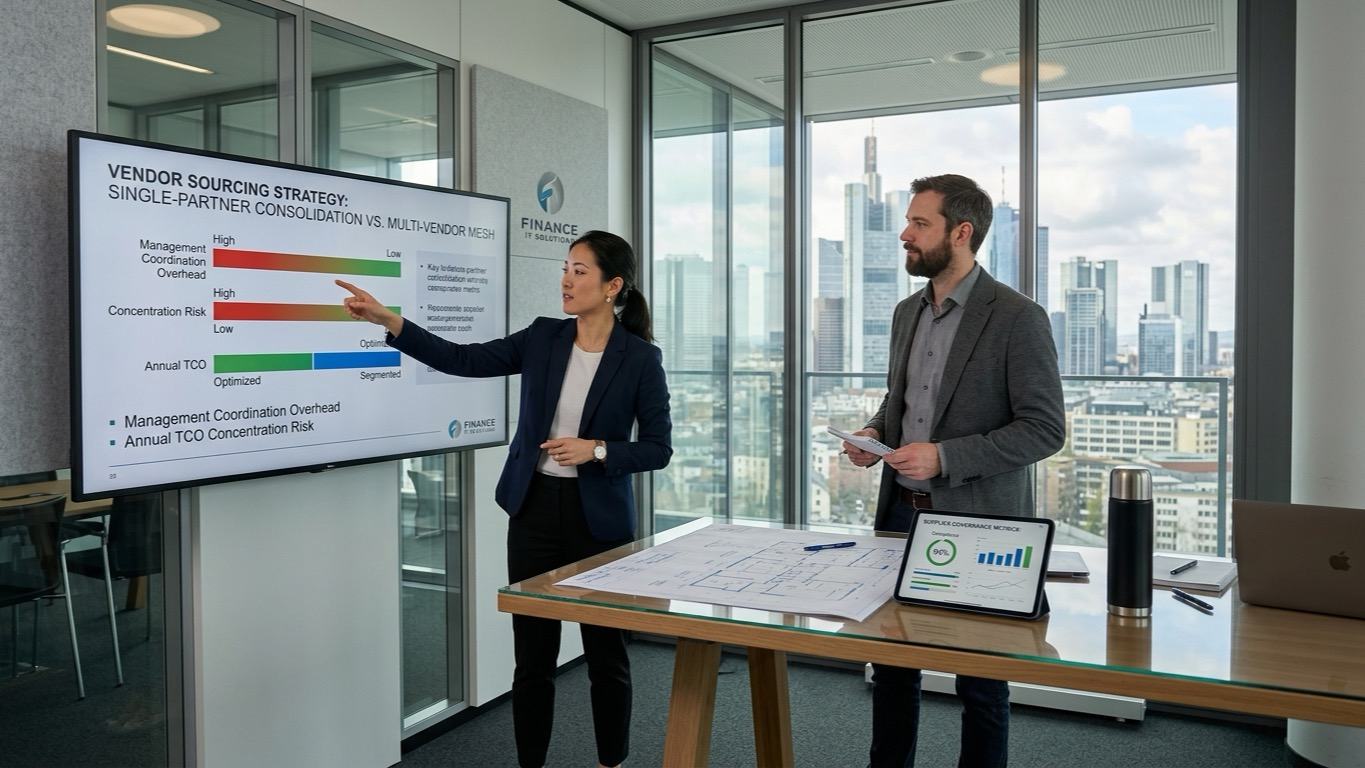
If your single development vendor disappeared tomorrow — lost their biggest client, got acquired, had a founder walk away — how many weeks of delivery would you lose before a replacement was even ramped? For most IT managers running on one outsourcing partner, the honest answer is uncomfortable, and it is the exact question that pushes procurement conversations toward a multi-vendor model. But splitting work across vendors trades one risk for a different set of costs, and the decision is rarely as simple as “diversification is safer.”
You are likely facing this decision because something has already made single-vendor concentration visible as a risk — a vendor capacity crunch during your busiest quarter, a security incident at a supplier that made your CISO ask uncomfortable questions about your own supply chain, or simply a board that has started using the word “resilience” in vendor reviews. This article works through the real trade-offs: what a multi-vendor strategy actually protects you against, what it costs you in coordination overhead that rarely shows up in the initial business case, and where the genuine break-even point sits for a mid-sized organization.
What Concentration Risk Actually Costs You
Single-vendor concentration is not a theoretical risk — it is a specific, quantifiable exposure. If one vendor holds architecture knowledge, deployment credentials, and delivery capacity for your core systems, a disruption on their end — from insolvency to a mass departure of senior engineers to a ransomware incident in their own environment — becomes your outage, your delay, your breach notification. In a 2025 review of mid-market IT incidents, supply-chain-adjacent disruptions (a vendor or subcontractor issue cascading into the buyer’s operations) accounted for a rising share of reported service disruptions, and organizations with a single development partner recovered measurably slower than those with an alternate team already onboarded.
The exposure compounds under EU regulatory pressure. If your company falls under DORA (Digital Operational Resilience Act) as a financial entity or a critical ICT third-party dependency, or under NIS2’s broader supply-chain risk requirements, regulators increasingly expect documented evidence that a single point of failure in your technology delivery chain has been assessed and mitigated — not just insured against. A single-vendor model that has never been stress-tested against “what if they can’t deliver next month” is an audit finding waiting to happen in a growing number of EU sectors.
The Coordination Tax Multi-Vendor Setups Actually Impose
The business case for diversification almost always undercounts coordination cost, and this is where multi-vendor strategies quietly fail. Every additional vendor touching a shared codebase or shared architecture introduces an integration seam: differing coding standards, different testing philosophies, different release cadences that must somehow converge on the same production environment. In practice, coordinating two vendors on tightly coupled systems adds a measurable tax — organizations running genuinely interdependent multi-vendor delivery report 10-20% more time spent on cross-team alignment meetings and integration debugging than single-vendor teams working the same scope.
The tax is smaller, sometimes close to zero, when the vendors are cleanly separated by domain rather than sharing a codebase — one vendor on the customer-facing web platform, another on internal data infrastructure, with a well-defined API boundary between them. The mistake IT managers make most often is splitting vendors along a line that looks clean on an org chart but is not clean in the code — two teams touching the same monolith, the same shared database schema, or the same deployment pipeline. That configuration produces the worst of both worlds: none of the risk reduction, all of the coordination overhead, plus finger-pointing when something breaks at the seam.
Where the Break-Even Point Actually Sits
For most mid-sized organizations, the break-even point is a function of system architecture, not headcount or budget size alone. If your technology estate is a single monolith or a tightly coupled set of services, the coordination tax of a multi-vendor split usually outweighs the risk-diversification benefit until you are large enough to absorb dedicated integration governance — typically north of 40-50 combined engineers across vendors, where a formal architecture review board and shared CI/CD standards become worth the overhead. Below that scale, splitting a monolith across vendors tends to produce net-negative delivery velocity.
If your architecture is already service-oriented or modular — separate services with well-defined contracts, independently deployable — the break-even point drops sharply, because the API boundary does the coordination work for you. In that scenario, even a 10-15 engineer organization can run two vendors cleanly: one on the core product, one on a clearly bounded satellite system like an admin portal, a data pipeline, or a mobile client. The architecture, not the org size, is the real gating factor.
The Case for Consolidation
Consolidating with a single, well-vetted vendor has real advantages that a risk-diversification narrative tends to undersell. A single vendor develops deep institutional knowledge of your codebase, your business logic, and your technical debt — knowledge that does not need to be re-explained at every hand-off boundary. Governance is simpler: one point of contact for security audits, one contract to negotiate, one relationship to invest in improving over time rather than several to maintain in parallel. For an IT manager already stretched across infrastructure, security, and application support, the operational simplicity of one relationship is not a minor convenience — it is often the difference between vendor management being 5% of the job or 20% of it.
Consolidation is the right call when your systems are tightly coupled, your internal team lacks the bandwidth for cross-vendor integration governance, and your chosen vendor has demonstrated the financial stability and staff depth (not a two-person shop, but a firm with bench capacity and defined succession for key roles) to make single-point-of-failure risk genuinely low rather than merely unexamined.
Structuring a Multi-Vendor Model That Actually Works
If diversification is the right call, structure it around clean boundaries rather than redundant coverage of the same system. Assign vendors by domain — a primary partner on core product development, a secondary partner on a clearly separated system or as a scoped backup for a specific critical function — and define the API or data contract between their areas of ownership in writing before either team starts building. Establish one internal owner (not a committee) responsible for cross-vendor technical alignment, and require both vendors to participate in a shared architecture review cadence, even if it is only monthly.
Avoid the common trap of maintaining two vendors purely as leverage in pricing negotiations without a real technical boundary between their work — this produces the coordination tax without meaningfully reducing concentration risk, since both vendors still depend on the same shared codebase failing or succeeding together.
Making the Final Call
Choose a single vendor when your architecture is tightly coupled and your team cannot absorb cross-vendor integration governance — the coordination tax will exceed the diversification benefit. Choose a multi-vendor model when your architecture is already modular, when a specific regulatory framework requires documented resilience against single-vendor failure, or when you are large enough to run a lightweight architecture review process across teams. The decision is not about how many vendors feels “safe” — it is about whether your system boundaries can absorb the seam a second vendor introduces.
Manifera works both models: as a sole delivery partner running full-stack ownership, or as a domain-scoped dedicated team operating cleanly alongside an existing internal or external team. If you are weighing which structure fits your architecture, our offshore software development team can walk through where your system boundaries actually sit.
Calculating Your Actual Concentration Exposure
Most IT managers stop the risk-diversification analysis at “the vendor could disappear” without pricing what a single-vendor outage actually costs. Run this instead: multiply your average weekly revenue tied to a vendor-maintained system by the realistic replacement ramp time — 3-4 weeks for a modular system with clean documentation, 10-14 weeks for an undocumented monolith — and you get concentration exposure in real terms. For a company doing €2M in annual revenue through a vendor-maintained system, a 10-week outage risk at even a conservative 15% revenue impact prices concentration risk above €55,000, which is the figure to weigh against the 10-20% coordination tax a second vendor adds to annual delivery spend.
Vendor consolidation strategies frequently skip this comparison and default to whichever option was cheaper last quarter, rather than modeling the tail risk. Recalculate the exposure figure at every contract renewal, not just when a vendor scare forces the conversation, and require any vendor holding sole custody of a revenue-critical system to demonstrate bench depth — at least three engineers who could pick up the account within two weeks of ramp — as a renewal condition rather than a nice-to-have.
FAQs
Is a multi-vendor strategy always safer than a single-vendor one?
No. A multi-vendor strategy reduces concentration risk only when vendors have clean, well-defined boundaries in the codebase. When two vendors share a tightly coupled system, you get the coordination overhead of multiple vendors without meaningfully reducing the risk that a failure on either side disrupts the whole system.
How many vendors should a mid-sized company use for software development?
Most mid-sized companies with a modular architecture do well with two: a primary vendor for core product development and a secondary vendor for a clearly bounded system, such as a data pipeline or an admin portal. Beyond two, coordination overhead tends to grow faster than any additional risk reduction justifies.
Does DORA or NIS2 require a multi-vendor strategy?
Neither regulation mandates a specific number of vendors, but both increasingly expect documented evidence that single points of failure in your technology supply chain have been identified and assessed. A single-vendor model can satisfy this if the assessment and mitigation plan exist and are current — it is the absence of that documentation, not the vendor count itself, that creates audit risk.
What is the biggest mistake companies make when splitting work across vendors?
The most common mistake is splitting vendors along an organizational line rather than an architectural one — for example, by feature team rather than by system boundary — which leaves two vendors touching the same shared codebase or database. This produces integration friction without genuine risk diversification.
How much extra does coordinating two vendors typically cost?
On tightly coupled systems, expect 10-20% more time spent on cross-team alignment and integration debugging compared to a single vendor working the same scope. On cleanly separated systems with a well-defined API boundary, this overhead can drop close to zero.
(Scenario: evaluating whether to consolidate an entire stack with one vendor) How do I verify a vendor’s bench depth before consolidating my whole stack with them?
Ask for named backup engineers who have actually touched your codebase in the past quarter, not just a headcount figure, and request evidence of at least one internal rotation or handoff on your account. A vendor that cannot name a second engineer familiar with your systems has effectively no bench, regardless of company size.
(Scenario: two vendors left sharing one monolith after an acquisition) We inherited two vendors on the same monolith after an acquisition — how do we fix it?
Don’t try to run both indefinitely on the shared codebase; pick one to own the monolith outright within one quarter and reassign the other to a cleanly bounded satellite system or transition them out. A shared monolith with two vendors compounds the coordination tax without any risk-diversification benefit, since a failure on either side can still break the whole system.
(Scenario: procurement wants a second vendor purely for negotiating leverage) Is it worth adding a second vendor purely to create pricing leverage on the first?
Only if you also give the second vendor a real, separately-owned piece of the system. Otherwise you pay the full coordination tax for a negotiating tactic that a documented benchmark and a competitive renewal clause could achieve for free.
(Scenario: presenting a vendor-count decision to the board) What should I show the board when justifying a single-vendor versus multi-vendor decision?
Present the concentration-exposure calculation in euros alongside the coordination-tax percentage for the alternative, not a qualitative risk narrative — boards respond to comparable numbers, and a documented exposure figure also satisfies the resilience-assessment expectation regulators like DORA and NIS2 increasingly look for.
Suggested Posts



How useful was this post?
Share it with your friends


Get our latest articles here!
Thank you for subscribing to our blog!
Do you have any questions?
Help us improve the content of this Insightful blog by asking us questions. Manifera's team of experts will help you answer these questions as soon as possible.
