
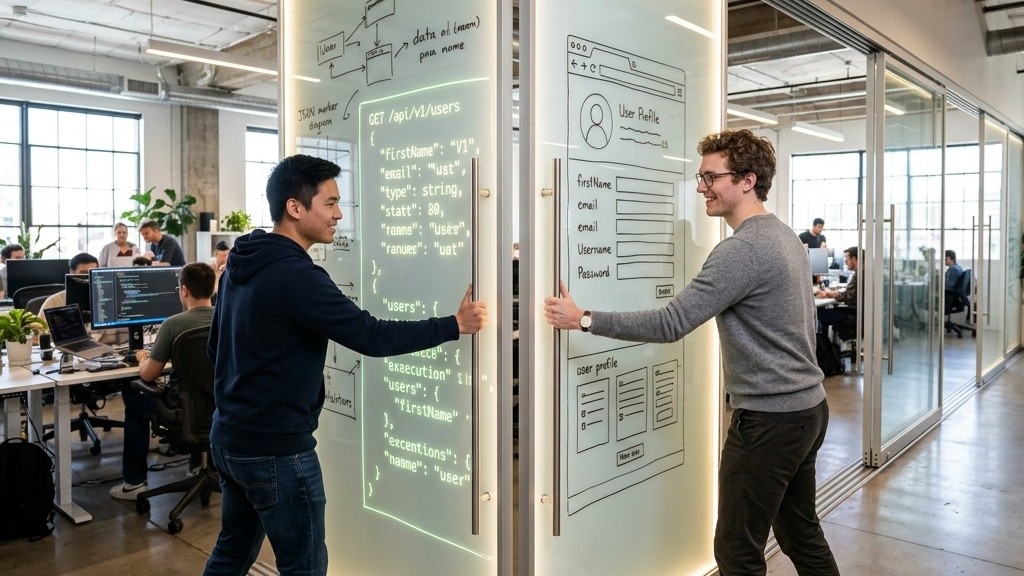
Your CRM cannot talk to your billing system. Your mobile app calls a different endpoint than your web app for the same data. Your partner wants to integrate, but there is no documentation and your internal APIs return inconsistent response formats. This is what happens when APIs are an afterthought — bolted on after the application is built instead of designed first.
API-first architecture inverts this approach: you design the API contract before writing a single line of application code. The API becomes the product. The web app, mobile app, and third-party integrations are all equal consumers of that product.
Why API-First Matters More in 2026
The scale of enterprise integration has become genuinely hard to overstate. Okta’s 2025 Businesses at Work report — which tracks app usage across thousands of customer organisations — found that the average company now runs 101 different applications, crossing the 100-app threshold for the first time — a jump that followed several years of the average sitting flat below 90, not a steady climb, which suggests the ecosystem is now expanding in sudden bursts rather than gradually. Salesforce connects to HubSpot connects to Slack connects to your custom analytics dashboard, and every one of those connections is an API call your software either supports cleanly or forces a partner to hack around. If your software cannot participate in this ecosystem seamlessly, it becomes an isolated island that enterprise buyers increasingly will not purchase — procurement checklists now routinely ask for API documentation before a demo is even scheduled.
The business case is straightforward:
- Faster, less error-prone development. When frontend and backend teams agree on the API contract upfront, they can work in parallel against a shared, machine-readable specification instead of a shifting target. The frontend team builds against mock responses while the backend team implements the real logic, which removes the largest source of late-stage integration rework: teams discovering, days before launch, that the frontend expected a shape the backend never agreed to build.
- Easier partner integrations. A well-designed public API turns every potential partner into a distribution channel. Stripe’s early growth is widely credited in the developer tooling industry to how cleanly its API was designed — developers chose it over competitors with comparable pricing because integration friction was near zero.
- Future-proofing. When you need to build a mobile app, a CLI tool, or support a webhook integration, the API already exists. You are adding a new client, not rebuilding the backend.
The Contract-First Design Process
API-first does not mean “write the API code first.” It means “design the contract first.” The contract is a machine-readable specification (typically OpenAPI 3.1 or GraphQL SDL) that defines every endpoint, request format, response format, and error code before implementation begins.
The workflow:
- Product defines the user story. “As a partner, I need to retrieve a customer’s invoice history filtered by date range.”
- Backend and frontend jointly design the contract.
GET /v1/customers/{id}/invoices?from=2026-01-01&to=2026-06-30returns a paginated list of invoice objects. - The contract is reviewed and approved. Like a code review, but for the API surface. Does the naming follow conventions? Is the response shape consistent with other endpoints? Are error codes standardised?
- Both teams build simultaneously. Frontend builds against the contract using mock servers (Prism, WireMock). Backend implements the contract. When both are done, integration is nearly frictionless because the contract was agreed upon in advance.
REST vs GraphQL vs gRPC: The 2026 Decision Matrix
The “REST vs GraphQL” debate has matured. The answer in 2026 is almost always: “It depends on your use case.”
| Criterion | REST | GraphQL | gRPC |
|---|---|---|---|
| Best for | Public APIs, CRUD operations | Complex frontends, mobile apps with bandwidth constraints | Internal microservice communication |
| Learning curve | Low | Medium | High |
| Caching | Excellent (HTTP caching) | Complex (requires Apollo/Relay) | Manual |
| Tooling maturity | Excellent | Very good | Good |
| Real-time support | Webhooks, SSE | Subscriptions (built-in) | Bi-directional streaming |
| Overfetching | Common problem | Solved by design | N/A (schema-defined) |
The pragmatic approach: Use REST for your public API (lowest barrier for integrators), GraphQL for your own frontend (optimal data fetching), and gRPC for internal service-to-service communication (maximum performance). These are not mutually exclusive — many mature platforms use all three.
The API Maturity Model: Diagnosing How “RESTful” Your API Actually Is
Most teams that claim to have “a REST API” have actually built something closer to RPC-over-HTTP: a single endpoint per action, verbs baked into the URL (/getInvoice, /updateCustomer), and a 200 status code regardless of what actually happened. This is not a cosmetic issue — it is the difference between an API that plays well with generic tooling (caching proxies, API gateways, client SDK generators) and one that requires custom integration code from every single partner.
The Richardson Maturity Model, introduced by Leonard Richardson in a 2008 conference talk and popularised in a widely-cited 2010 article by Martin Fowler, gives a concrete way to diagnose this. It defines four levels of REST adoption:
The pragmatic target for 2026: Level 2 is the right destination for the large majority of B2B APIs. It gets you correct HTTP caching, predictable error handling, and out-of-the-box compatibility with every API gateway and SDK generator on the market — the same level Stripe, Twilio, and GitHub operate at. Level 3 is rarely worth the added client-side complexity unless your API genuinely needs to evolve its available actions without forcing a version bump, which is a narrow use case for most B2B products. Use the model as a self-audit: pull five endpoints from your existing API at random and score each one. If more than one lands at Level 0 or 1, that is your most cost-effective refactoring target before investing further in documentation or partner onboarding — fixing the verb and status-code layer is cheap early; fixing it after twenty partners have integrated against the wrong contract is not.
Versioning: The Hardest Problem in API Design
Nothing destroys partner trust faster than a breaking API change. When Twilio or Stripe ships a new API version, the old version continues working for years. This is not generosity — it is strategic necessity. Every breaking change forces every integration partner to spend engineering hours updating their code, and some will choose to switch providers instead.
Versioning strategies ranked by pragmatism:
-
URL versioning (
/v1/,/v2/). Simple, visible, easy to route. The most common approach and the one we recommend for most teams. When you introduce/v2/, keep/v1/running for a minimum of 18 months with a documented sunset timeline. -
Header versioning (
Accept: application/vnd.api+json; version=2). Cleaner URLs but harder to test in a browser and less discoverable. Good for internal APIs. -
Query parameter versioning (
?version=2). Easy to implement but pollutes the query string. Acceptable for simple APIs.
The golden rule of versioning: Adding a new field to a response is not a breaking change. Removing a field, renaming a field, or changing a field’s type is a breaking change. Design your responses with extensibility in mind — use objects instead of arrays for top-level responses, include a meta field for pagination, and never return bare lists.
Documentation as a Product
An API without documentation is an API without users. Yet the majority of internal APIs have documentation that is either non-existent, outdated, or generated from code annotations that describe what the API does but not how to use it.
The documentation hierarchy:
- Reference documentation (auto-generated from OpenAPI spec). Lists every endpoint, parameter, and response. Necessary but not sufficient.
- Getting started guide. A tutorial that takes a new developer from zero to their first successful API call in under 10 minutes. This is the single most impactful piece of documentation you can write.
- Use case guides. “How to build an invoice dashboard,” “How to set up webhook notifications.” These connect technical endpoints to business outcomes.
- Changelog. Every API change, no matter how small, documented with the date, the change description, and the migration path.
Tools like Redoc, Swagger UI, and Stoplight generate beautiful interactive documentation directly from your OpenAPI spec. Invest 2 days in setting this up — it will save hundreds of hours in support tickets from integration partners.
Rate Limiting, Authentication, and the Operational Details That Matter
A technically perfect API that falls over under load or leaks customer data is worse than no API at all. The operational details matter:
Rate limiting: Implement tiered rate limits (e.g., 100 requests/minute for free tier, 1,000 for paid, 10,000 for enterprise). Return clear 429 Too Many Requests responses with a Retry-After header. Document the limits prominently.
Authentication: Use OAuth 2.0 with short-lived access tokens and long-lived refresh tokens for user-context APIs. Use API keys with scoped permissions for server-to-server integrations. Never pass credentials in query parameters — always use headers.
Error responses: Standardise your error format. Every error response should include: a machine-readable error code, a human-readable message, and a documentation URL. Stripe’s error responses are the gold standard — study them.
Building API-First Across Distributed Teams
When your engineering team spans Amsterdam and Ho Chi Minh City, API-first architecture becomes even more critical. The API contract serves as a shared source of truth that transcends time zones and language barriers.
At Manifera, our distributed development model treats the API specification as the primary coordination document between European product teams and Vietnamese engineering teams. The contract is designed and reviewed during overlap hours (14:00-17:00 CET), then both teams build against it independently — frontend in Europe, backend in Vietnam, meeting at integration with minimal friction.
Interested in building an API-first architecture with a team that has done it dozens of times? Contact our Amsterdam office — manifera.com/contact-us.
FAQs
How do we migrate an existing application to API-first without rewriting everything? (Scenario: CTO with a 5-year-old monolith that has no public API)
Start by identifying the three most requested integration use cases. Build API endpoints for only those three use cases, documented with OpenAPI specs. Route them through an API gateway (Kong, AWS API Gateway) that sits in front of your existing application. This gives you a clean API surface without touching the monolith internals. Expand the API surface incrementally — adding 2-3 endpoints per sprint based on partner demand.
Should we use OpenAPI or GraphQL SDL for our API specification? (Scenario: Engineering lead choosing a spec format for a new platform)
Use OpenAPI 3.1 if your primary consumers are external partners or third-party developers — it is the industry standard, has the broadest tooling support, and generates client SDKs in every major language automatically. Use GraphQL SDL if your primary consumers are your own frontend teams and you need the flexibility of client-specified queries. For most B2B SaaS products, OpenAPI is the safer choice because enterprise customers expect REST APIs.
How many API versions should we support simultaneously? (Scenario: Product Manager planning a major API overhaul that will break backward compatibility)
Support a maximum of two major versions concurrently: the current version and the previous version. Announce the deprecation of the old version at least 12 months before sunsetting it. Provide a migration guide with code examples for every breaking change. Monitor usage of the deprecated version — if fewer than 5% of API calls use the old version after 6 months, you can accelerate the sunset timeline.
What is the right team structure for API-first development? (Scenario: VP Engineering reorganising teams around a new platform strategy)
Assign API ownership to a dedicated “platform team” of 2-3 senior engineers who own the API specification, review all contract changes, and maintain documentation. Feature teams consume and extend the API but cannot modify the contract without platform team approval. This prevents the API from becoming inconsistent as multiple teams add endpoints independently. The platform team is the API’s product manager.
How do we ensure API quality across distributed development teams? (Scenario: CTO managing API development between Amsterdam and Ho Chi Minh City offices)
Three mechanisms: (1) Contract-first development — both teams build against the agreed OpenAPI spec, eliminating ambiguity. (2) Automated contract testing — tools like Pact or Dredd verify that the implementation matches the specification on every build. (3) API style guides — document naming conventions, pagination patterns, and error formats so every endpoint feels consistent regardless of which team built it. At Manifera, our cross-timezone API reviews happen during daily overlap hours to ensure alignment.
How do we know if our existing API is actually good, or just “technically REST”? (Scenario: CTO inheriting a legacy API with vague documentation and inconsistent behaviour)
Score it against the Richardson Maturity Model. Pull 5-10 endpoints at random and check: Do they use proper resource-based URLs (Level 1)? Do they use correct HTTP verbs and status codes instead of always returning 200 with an error buried in the body (Level 2)? Most commercially successful B2B APIs — including Stripe, Twilio, and GitHub’s — operate at Level 2, which is the pragmatic target for the large majority of teams. If your audit finds endpoints stuck at Level 0 (a single POST endpoint with the real action encoded in the payload), that is the highest-leverage place to invest refactoring effort before adding new features or onboarding more partners.
Suggested Posts



How useful was this post?
Share it with your friends


Get our latest articles here!
Thank you for subscribing to our blog!
Do you have any questions?
Help us improve the content of this Insightful blog by asking us questions. Manifera's team of experts will help you answer these questions as soon as possible.
